forge-sec API Vulnerability Scanner

Discover API ExposureValidate Real Risk

Discover your API attack surface, test authenticated operations, validate exploitable weaknesses, and give developers the evidence they need to fix risk quickly.

Complete endpoint discovery Auth-aware testing Evidence-backed findings
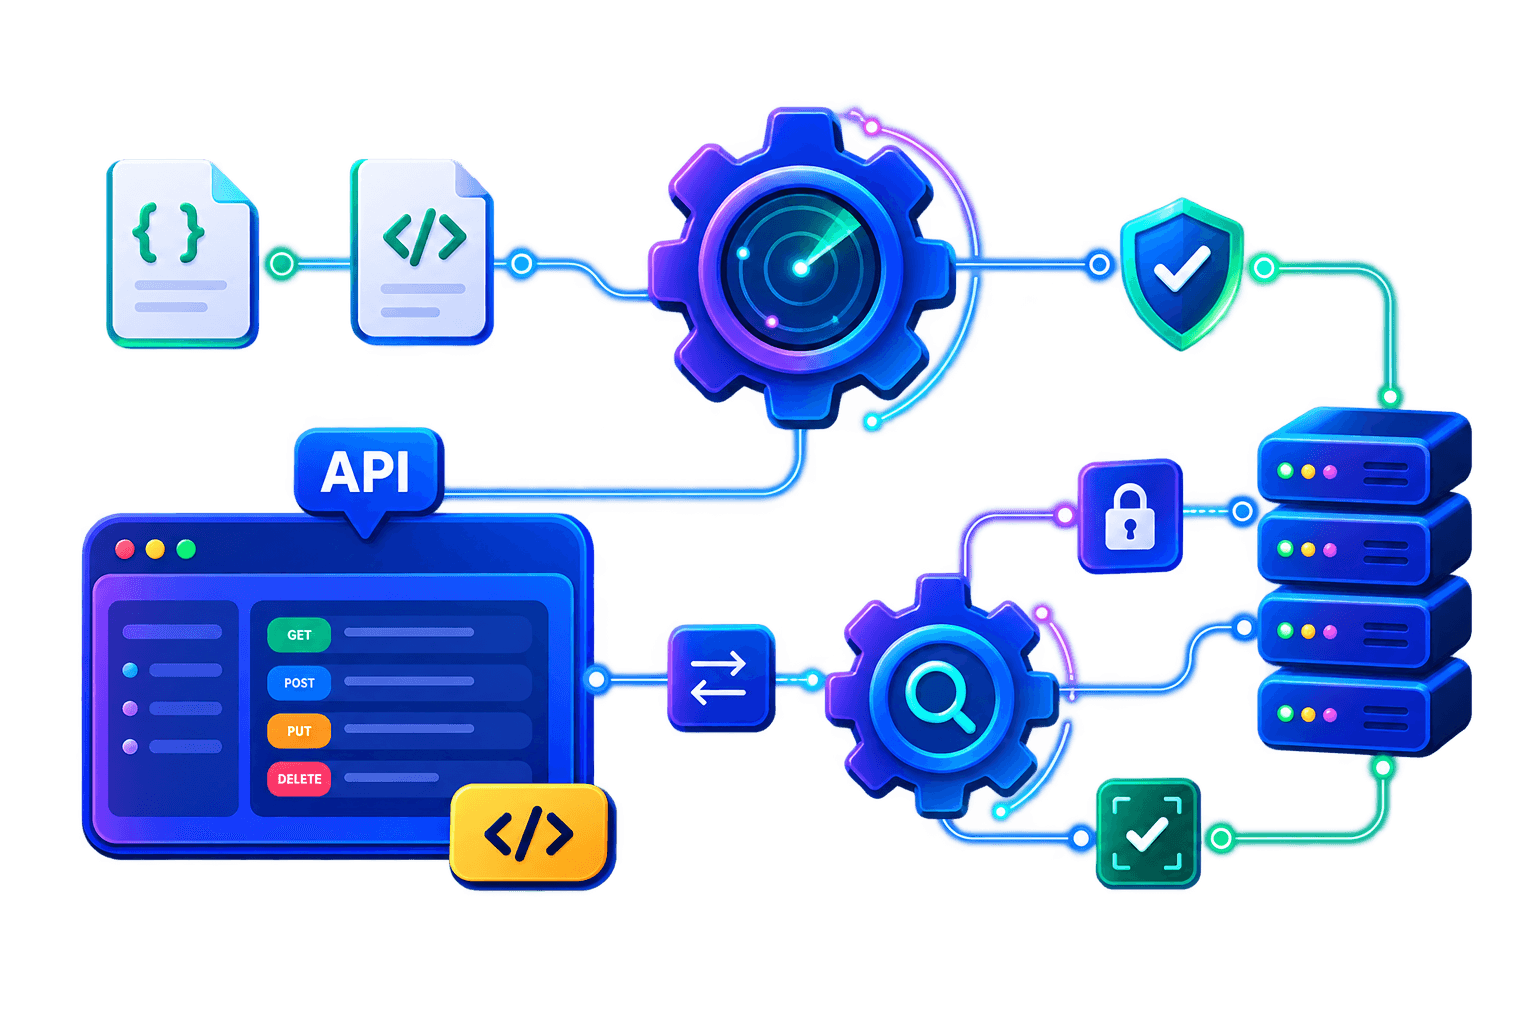
API scanner workflow connecting API specifications, testing engines, validation, and servers
API Attack Surface Discovery

Map Your API Attack Surface

APIs can expose hundreds of endpoints, parameters, authentication flows, and data objects. forge-sec builds a structured inventory of your API attack surface before security testing begins.

01PATH

Endpoint Inventory

Identify available API paths, HTTP methods, parameters, request bodies, content types, and expected responses. Build a complete, structured inventory that gives your team a reliable view of every operation exposed across the API environment.

02SPEC

Specification Analysis

Analyze OpenAPI and Swagger files to understand API structure, authentication requirements, server URLs, deprecated operations, and required test values. Validate documented behavior against the live implementation to uncover missing or inconsistent coverage.

03AUTH

Authentication Mapping

Determine which endpoints are public, protected, or incorrectly exposed and identify the authentication methods associated with each operation. Map tokens, roles, and access requirements so authorization testing reflects real user and service boundaries.

04SHADOW

Shadow and Deprecated APIs

Highlight undocumented, outdated, forgotten, or inconsistently protected endpoints that may increase your organization’s exposure. Surface operations that remain reachable outside the approved specification or normal development lifecycle.

Real-World API Security Testing

Identify API Weaknesses Validate Real Risk

forge-sec performs controlled security testing across authorized API endpoints and analyzes live responses to identify vulnerabilities that could expose sensitive data, business functions, or backend systems.

It tests path parameters, query strings, headers, authentication tokens, cookies, and request bodies for broken access control, authentication weaknesses, injection risks, unsafe input handling, missing rate limits, excessive data exposure, server-side request risks, and security misconfigurations.

Every validated vulnerability includes the affected endpoint, HTTP method, vulnerable input, severity, potential impact, supporting request-and-response evidence, and clear remediation guidance—so teams can fix and confidently retest the endpoint.

CONTROLLED TESTLIVE RESPONSE ANALYSIS
GET/api/v1/accounts/{accountId}200 OK
PATH PARAMETERQUERY STRINGAUTH TOKENHEADERSCOOKIESREQUEST BODY
VALIDATED FINDINGBroken Object-Level Authorization

Resource returned outside the authorized account scope.

HIGH
Evidence captured Remediation ready Retest supported
Actionable Security Reports

Turn Validated API Risk Into Action

forge-sec converts raw scanner output into structured reports with validated evidence, risk context, and practical guidance for every team involved.

Validated evidence Risk prioritized Fix guidance included
01

Prioritize the Most Important API Risks

Organize validated vulnerabilities by severity, exploitability, affected API service, authentication context, and potential impact—so teams can focus on the risks that require action first.

  • Risk contextSeverity and exploitability
  • API exposureService and authentication scope
  • Business impactData and operations at risk
02

Reports for Every Security Role

Give developers technical evidence, leaders a clear risk summary, and compliance teams structured records—all from the same validated security data.

  • DevelopersEvidence and remediation steps
  • LeadershipRisk and priority summaries
  • ComplianceStructured audit documentation
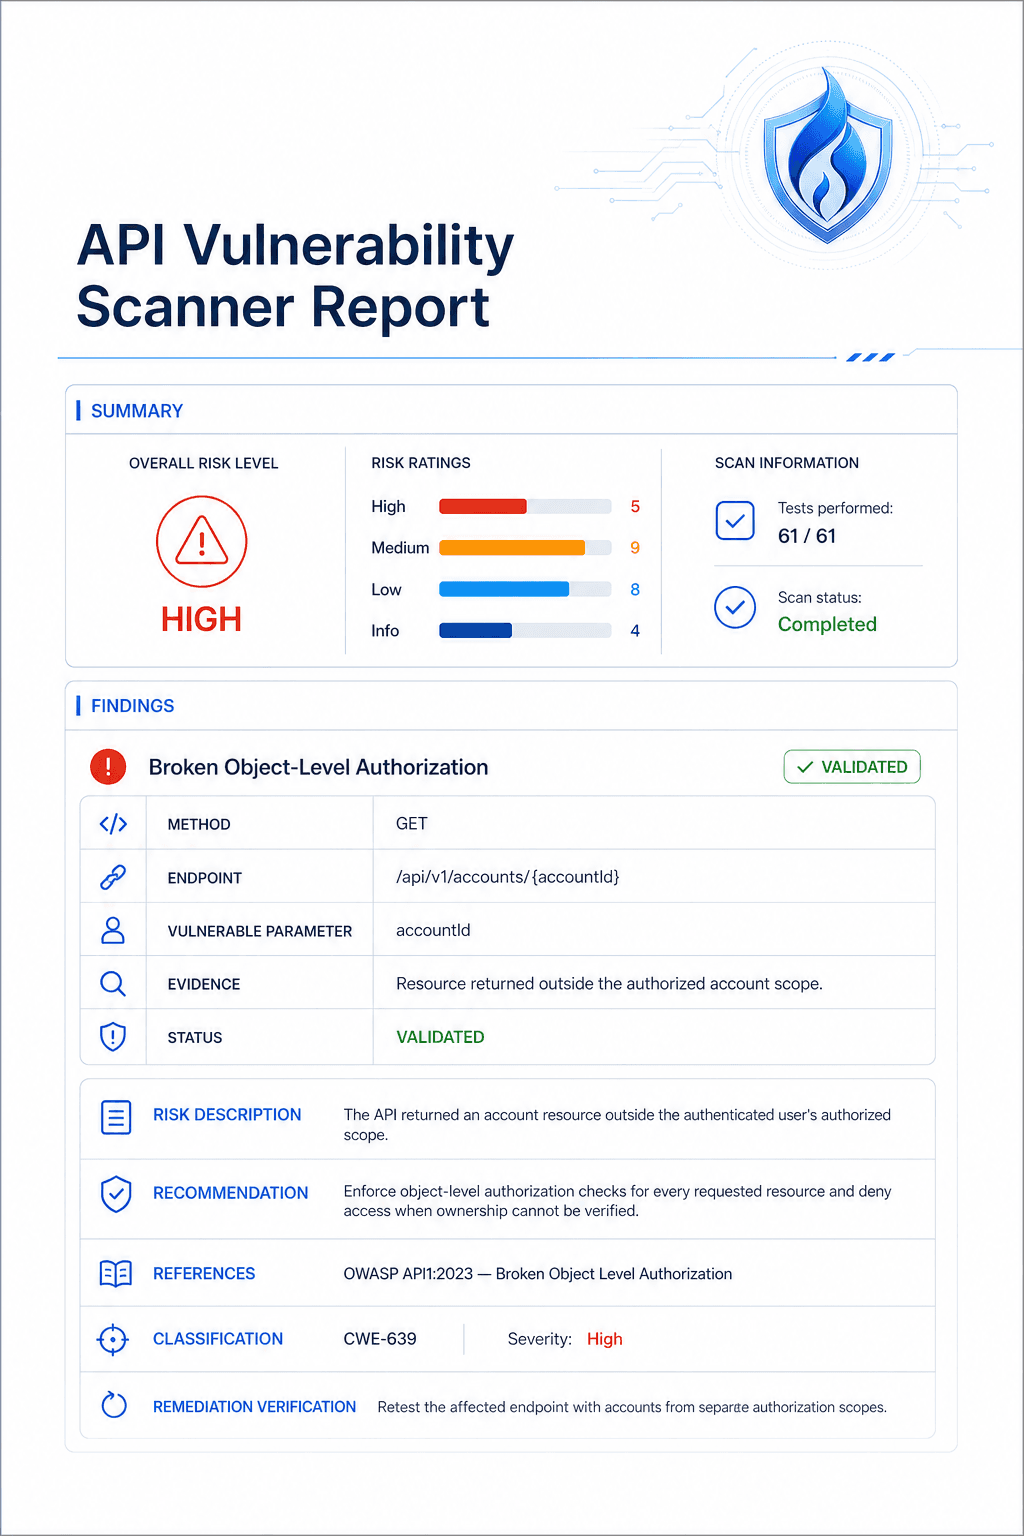
Sample API Security ReportEvidence-backed findings, ready to share
PDF
forge-sec API vulnerability scanner report showing risk distribution, scan information, and a validated authorization findingforge-sec
Continuous Vulnerability Monitoring

Track API Risk Across Every Release

APIs change frequently as developers introduce new endpoints, update authentication logic, modify request schemas, and deploy new integrations. forge-sec helps your team continuously monitor these changes and detect risks throughout the API lifecycle.

01
AUTOMATE

Scheduled API Scans

Run API security scans automatically on a daily, weekly, monthly, or custom schedule without repeatedly configuring the target.

02
DISCOVER

Detect New and Changed Endpoints

Compare API specifications and scan results to identify newly introduced, modified, deprecated, or undocumented operations.

03
PRIORITIZE

Track New and Recurring Risks

Identify vulnerabilities introduced by recent releases, unresolved findings from previous scans, and security issues that return after deployment.

04
VALIDATE

Verify Remediation

Retest affected endpoints after fixes are deployed and confirm whether vulnerabilities have been resolved using updated evidence.

05
REPORT

Maintain API Scan and Validation History

Track API scans, findings, severity changes, remediation activity, and validation results from one centralized dashboard.