Pages, Forms & Parameters
Analyze application pages, forms, and parameters to reveal weaknesses hidden across your web application.
Continuously scan modern web applications, validate exploitable weaknesses, and help your team fix real risk with confidence.
forge-sec analyzes pages, forms, parameters, APIs, scripts, headers, authentication flows, and underlying technologies to reveal weaknesses hidden across your web application.
Analyze application pages, forms, and parameters to reveal weaknesses hidden across your web application.
Discover public and hidden pages, forms, parameters, JavaScript routes, directories, and connected endpoints across your application.
Identify common and critical weaknesses, including injection flaws, cross-site scripting, insecure configurations, exposed files, and outdated components.
Scan protected application areas using authorized login credentials and inspect session handling, access controls, and authenticated workflows.
Detect frameworks, servers, libraries, content management systems, security headers, TLS configuration, and third-party components.
Analyze APIs, scripts, and headers across connected application endpoints and underlying technologies.
forge-sec combines reconnaissance, intelligent crawling, vulnerability testing, and risk analysis in one controlled scanning workflow.
Enter a website URL, choose the scanning profile, define scope rules, and optionally provide authentication details.
The scanner maps pages, endpoints, parameters, forms, technologies, directories, and other accessible application assets.
forge-sec performs controlled security checks to identify weaknesses, misconfigurations, exposed resources, and known vulnerabilities.
Receive prioritized findings with severity, affected URLs, technical evidence, risk descriptions, and recommended remediation steps.
forge-sec transforms raw scanner findings into structured, actionable reports that developers, security teams, IT administrators, and decision-makers can understand and act on immediately.
Every finding includes a clear severity level, risk description, affected asset, technical impact, and step-by-step remediation guidance to help teams move from detection to resolution.
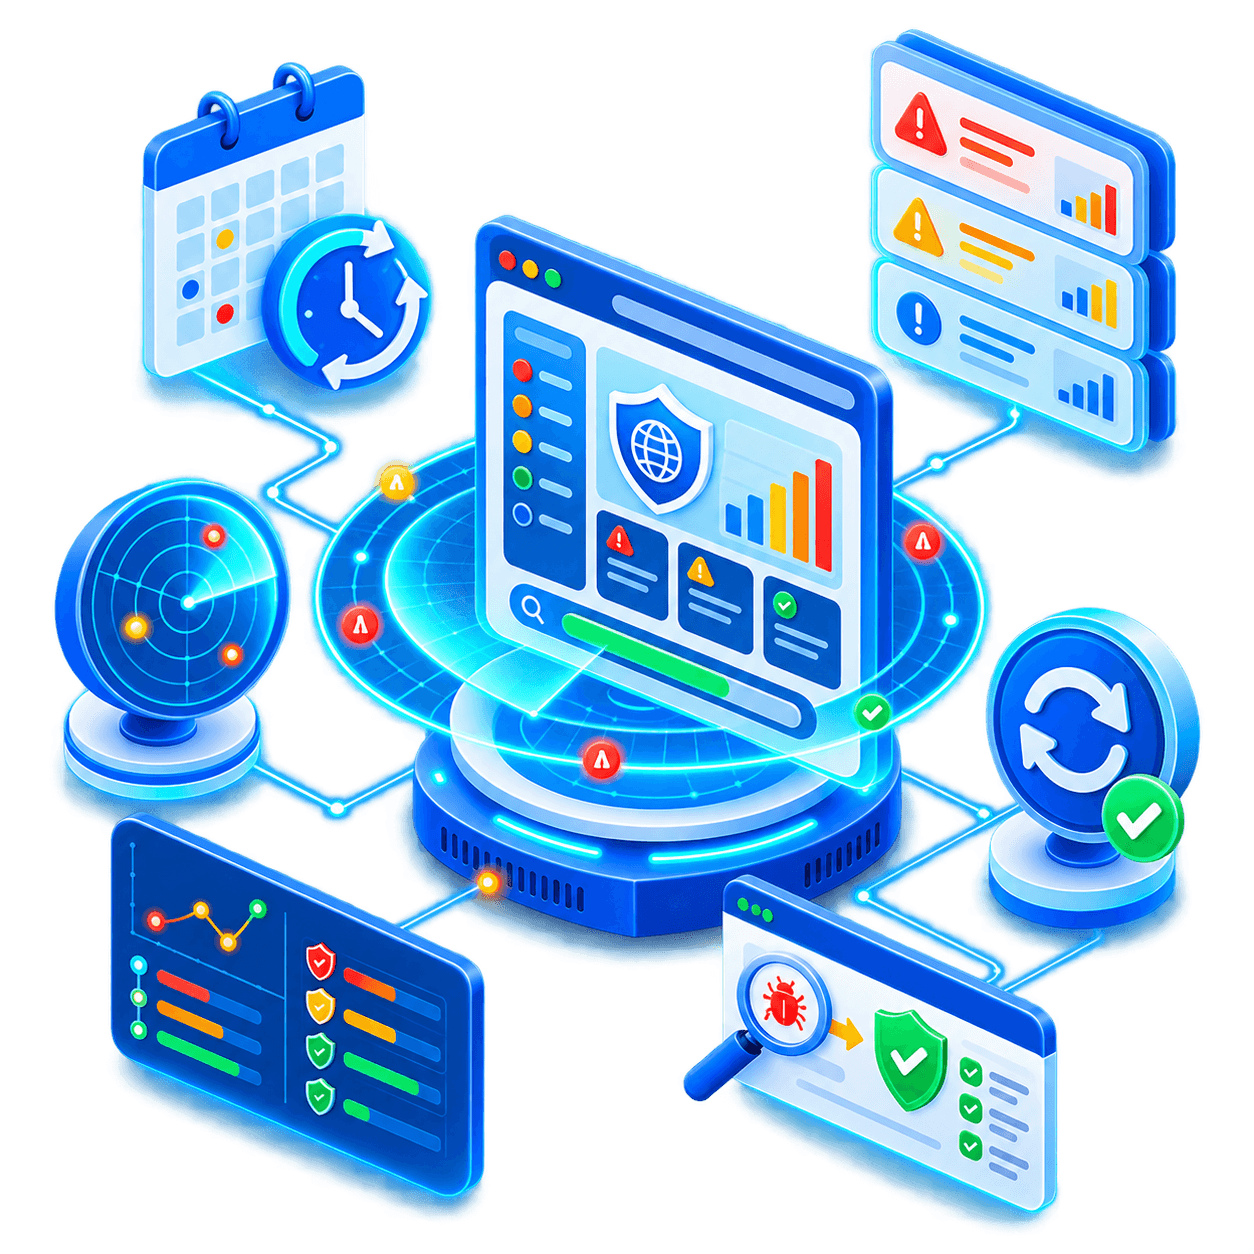
Web applications change constantly. New deployments, updated dependencies, configuration changes, and newly discovered vulnerabilities can introduce risks at any time. forge-sec continuously monitors your application and helps your team detect security issues before they reach attackers.
Maintain continuous visibility across releases, catch security regressions early, and give teams an audit-ready record of how application risk changes over time.
Run scans automatically on a daily, weekly, monthly, or custom schedule without repeatedly configuring the same target.
Compare scan results over time to identify newly discovered vulnerabilities, unresolved findings, and security issues that have returned after deployment.
Retest fixed vulnerabilities and confirm whether remediation was successful using updated evidence and scan results.
Track every scan, finding, status change, and remediation attempt from one centralized dashboard for better visibility and accountability.
Launch the forge-sec Website Vulnerability Scanner to discover exposed attack paths, validate real security risks, and receive proof-backed remediation guidance—all from one centralized platform.
Get continuous visibility into your website’s security posture and help your development and security teams resolve the vulnerabilities that matter most.