Discover Unknown Assets
Find forgotten subdomains, untracked applications, undocumented API endpoints, exposed hosts, and services missing from your inventory.
Your attack surface spans websites, APIs, servers, IP addresses, ports, services, and connected technologies. forge-sec brings them into one continuously updated, evidence-backed security view.
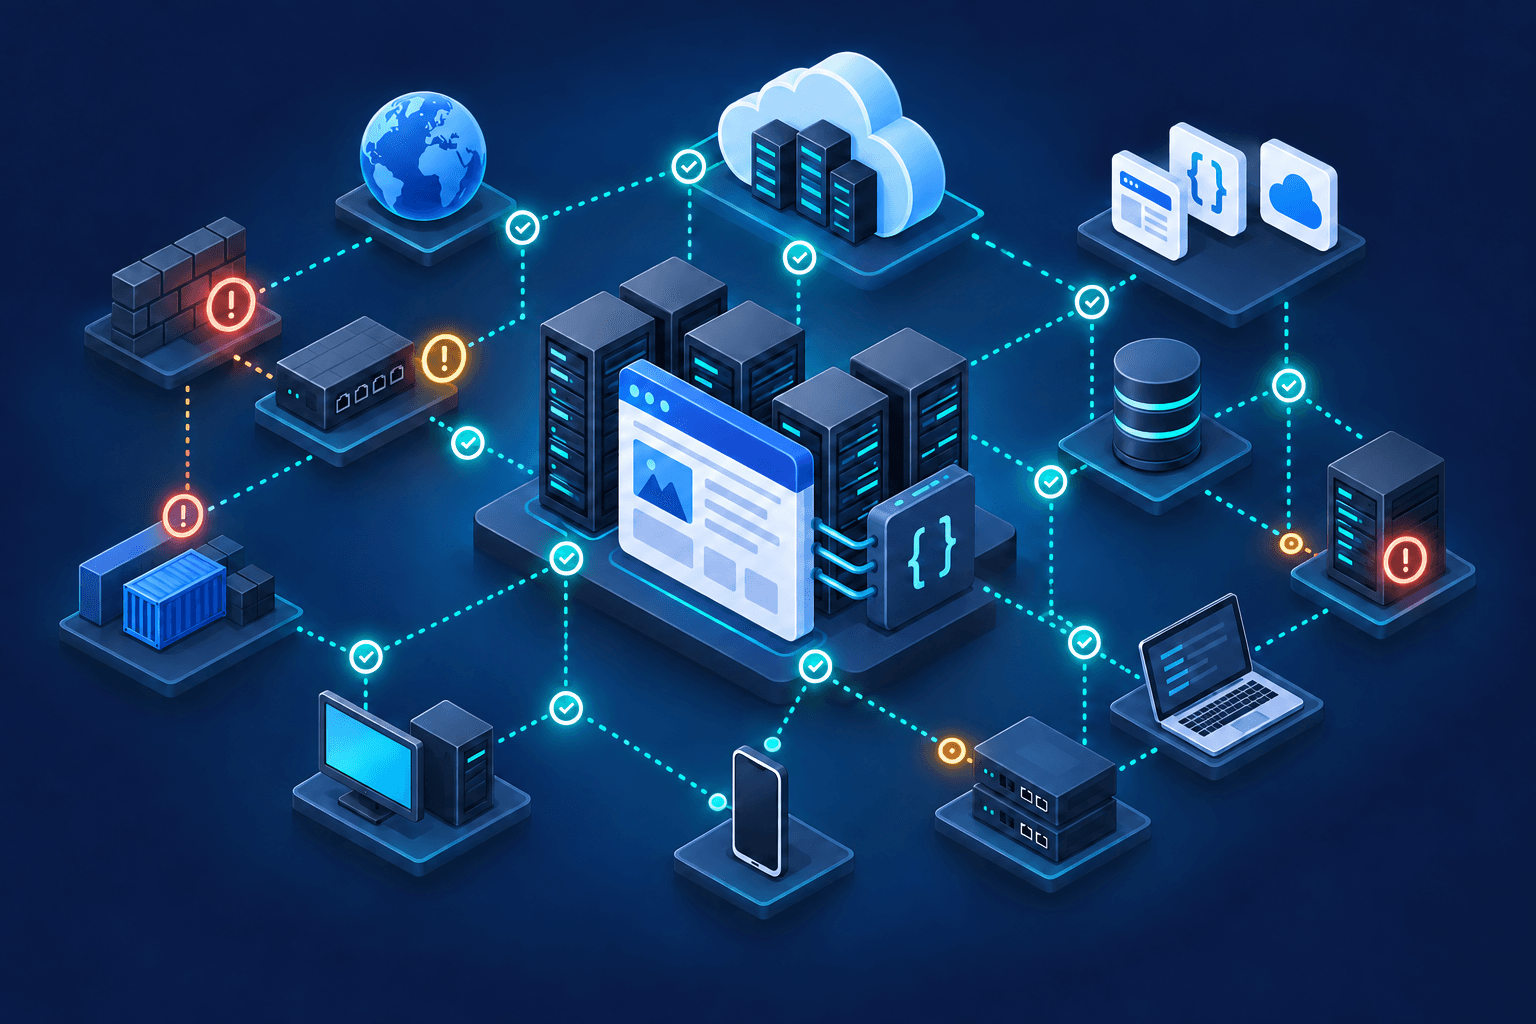
Your environment changes with every application, API, server, and public service, making static inventories quickly outdated. forge-sec continuously connects these assets into one current attack-surface inventory.
Find forgotten subdomains, untracked applications, undocumented API endpoints, exposed hosts, and services missing from your inventory.
See which assets and services are reachable from the internet and could become potential attacker entry points.
Detect web technologies, software versions, network services, operating systems, protocols, and connected components.
Track newly discovered assets, opened ports, changed services, modified technologies, and exposure drift between assessments.
An exposed asset is not automatically an urgent vulnerability. forge-sec tests authorized assets and correlates Web, API, and OS scanner signals with reachability, exploitability, technical evidence, and business importance.
Confirm weaknesses through controlled checks, response analysis, service detection, payload results, and technical evidence.
See whether an affected application, endpoint, port, or service is public, restricted, authenticated, or protected.
Identify how exposed services, vulnerable applications, insecure APIs, and host weaknesses combine into attack paths.
Rank findings using exploitability, asset importance, confidence, potential impact, and exposure—not severity alone.
forge-sec keeps every asset, exposure, vulnerability, and remediation action connected. Security teams gain complete visibility while engineering teams receive the evidence and guidance needed to resolve real risk.
Maintain asset visibility, validate vulnerabilities, assign ownership, track remediation, and confirm resolved weaknesses do not return.
Build a continuously updated attack-surface view and help every team focus on the exposures most likely to affect your organization.
Applications, APIs, domains, hosts, ports, certificates, and cloud services do not exist in isolation. forge-sec connects related assets, technologies, vulnerabilities, and dependencies so teams can see how an exposed entry point could lead toward sensitive systems.
Visualize how domains, APIs, servers, services, and technologies connect across your environment.
Find combinations of exposed services, weak controls, and validated vulnerabilities that lead toward critical systems.
Connect assets with responsible teams, business functions, exposure levels, and operational importance.
Review related assets, evidence, vulnerabilities, and remediation activity from one connected security view.
Continuously discover exposure, validate real risk, and guide remediation from one connected view.